Article verified for Release 16.1 on October 15, 2026
Roles and permissions define what users can access and do within the YouTestMe GetCertified application. Each role consists of a set of permissions and configurable settings that determine which features, actions, and information are available to users, helping administrators manage access and maintain system security.
This article explains the available default roles, how to create and manage custom roles, and how to configure role-specific settings, including permissions, landing pages, user registration, two-factor authentication, predefined reports, homepage widgets, and account security policies.
Default Roles
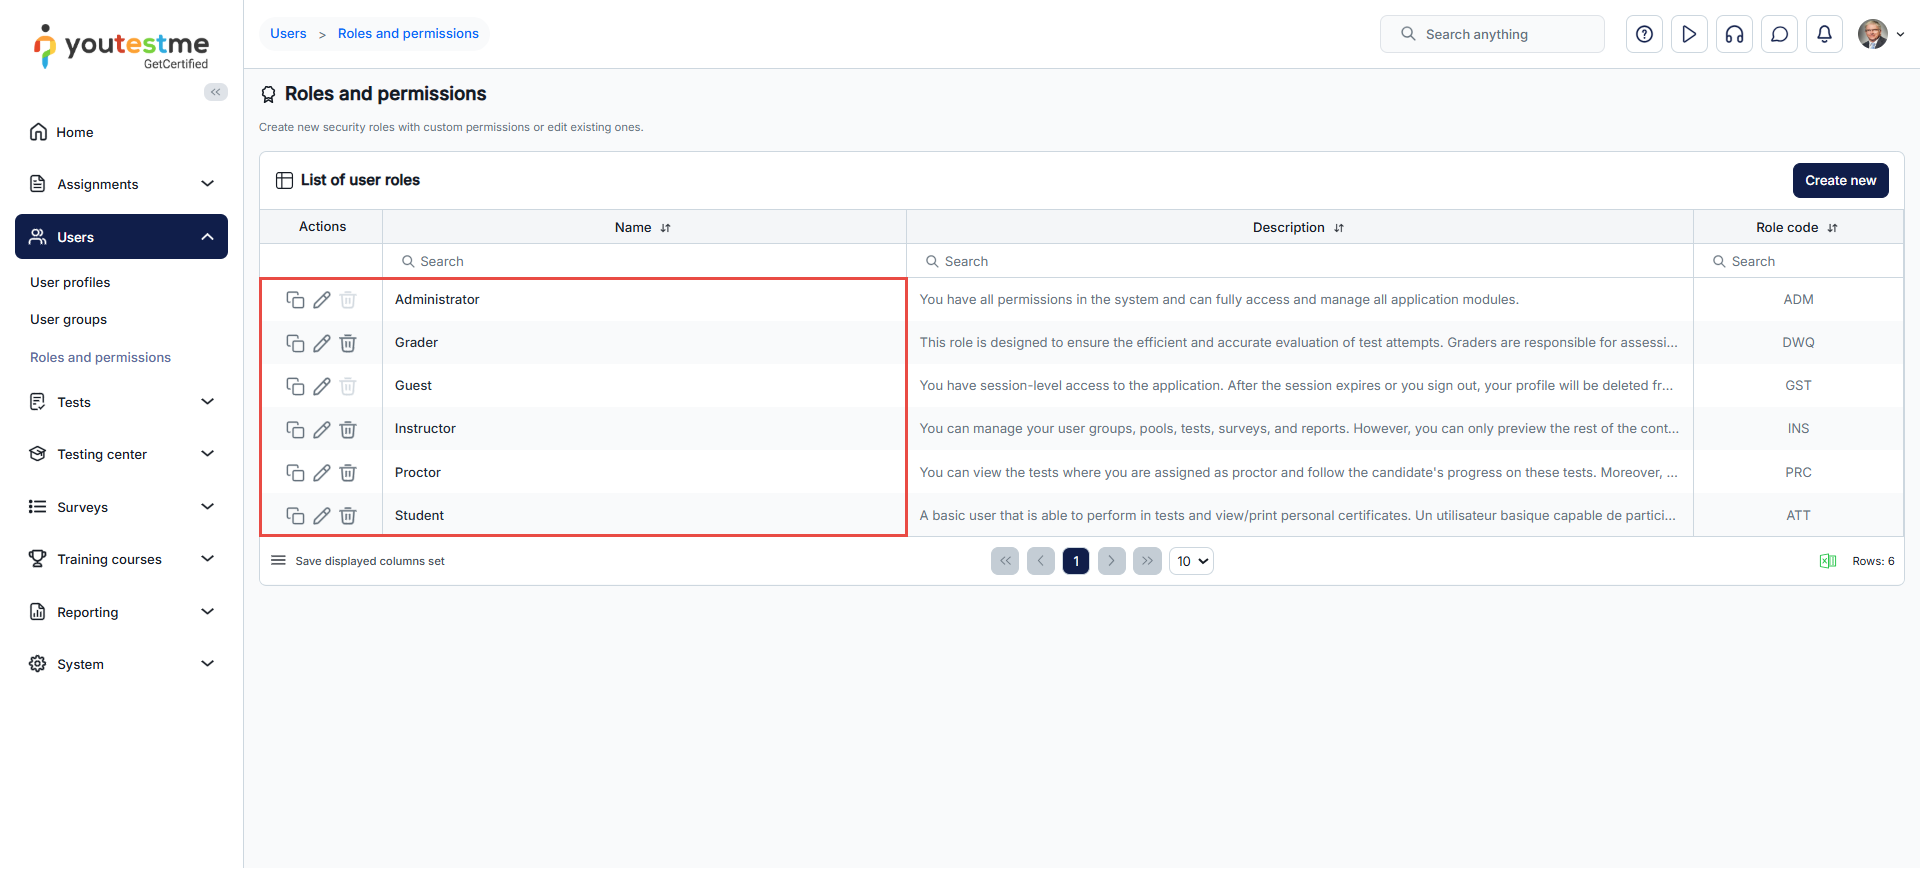
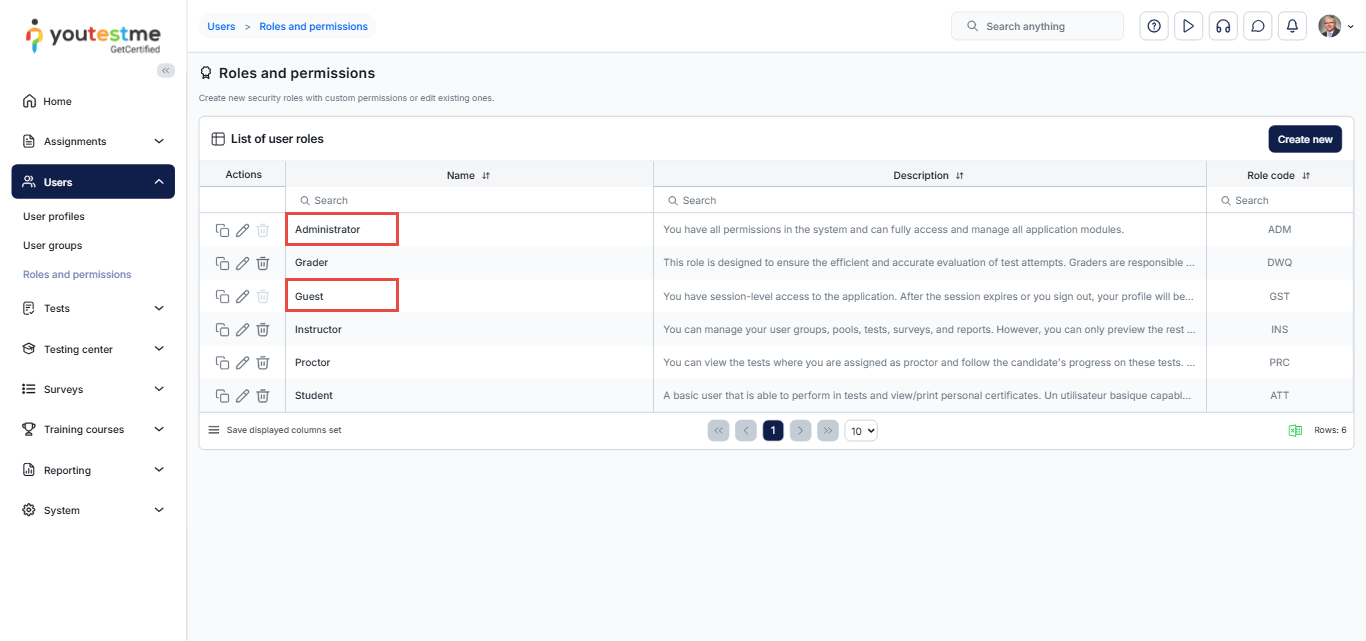
Predefined roles in the system are:
- Administrator -A role with all permissions in the system that can fully access and manage all application modules.
- Instructor – A role with higher-level permissions than a regular user. Instructors can manage groups, question pools, tests, and reports assigned to them, while only previewing the content not managed by them.
- Proctor – Proctors can monitor candidate progress on tests and supervise them in real-time.
- Student – A basic user who can take assigned tests, surveys, training courses, and view/print personal certificates.
- Guest- Provides temporary access for non-registered users to take tests and surveys, with no user data stored or actions recorded.
Non-editable Default Roles
The two default roles, Administrator and Guest, cannot be edited or deleted. This means you can only assign users to these roles; you cannot modify what they can access or how they function.
All other default roles (Instructor, Proctor, Student) are editable, allowing you to adjust their permissions if needed.
Custom Roles
In addition to the predefined options, you can edit the adjustable ones or create an unlimited number of custom roles. Custom roles let you define unique permission sets, landing pages, or registration rules that the default ones may not cover. 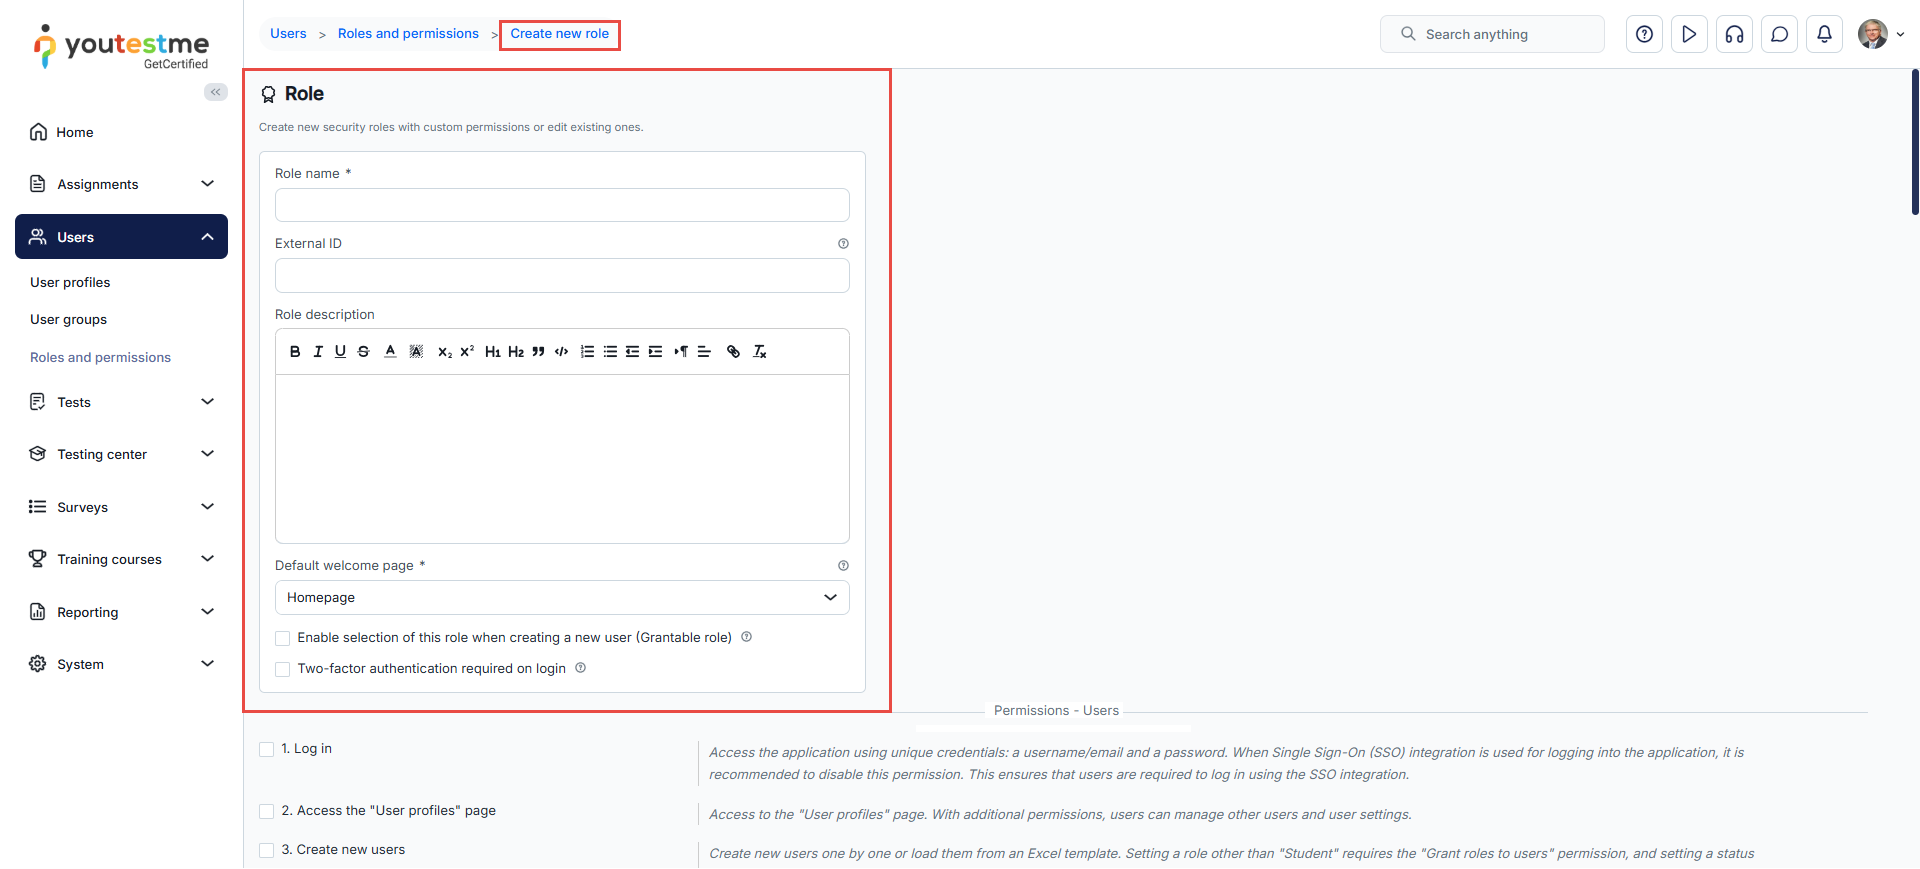
This flexibility allows you to rely on system defaults, tailor existing roles, or build new ones from scratch. A single user can have only one role per workspace, but can have different roles across multiple workspaces. For more details on workspace roles, please visit this article.
Managing Roles
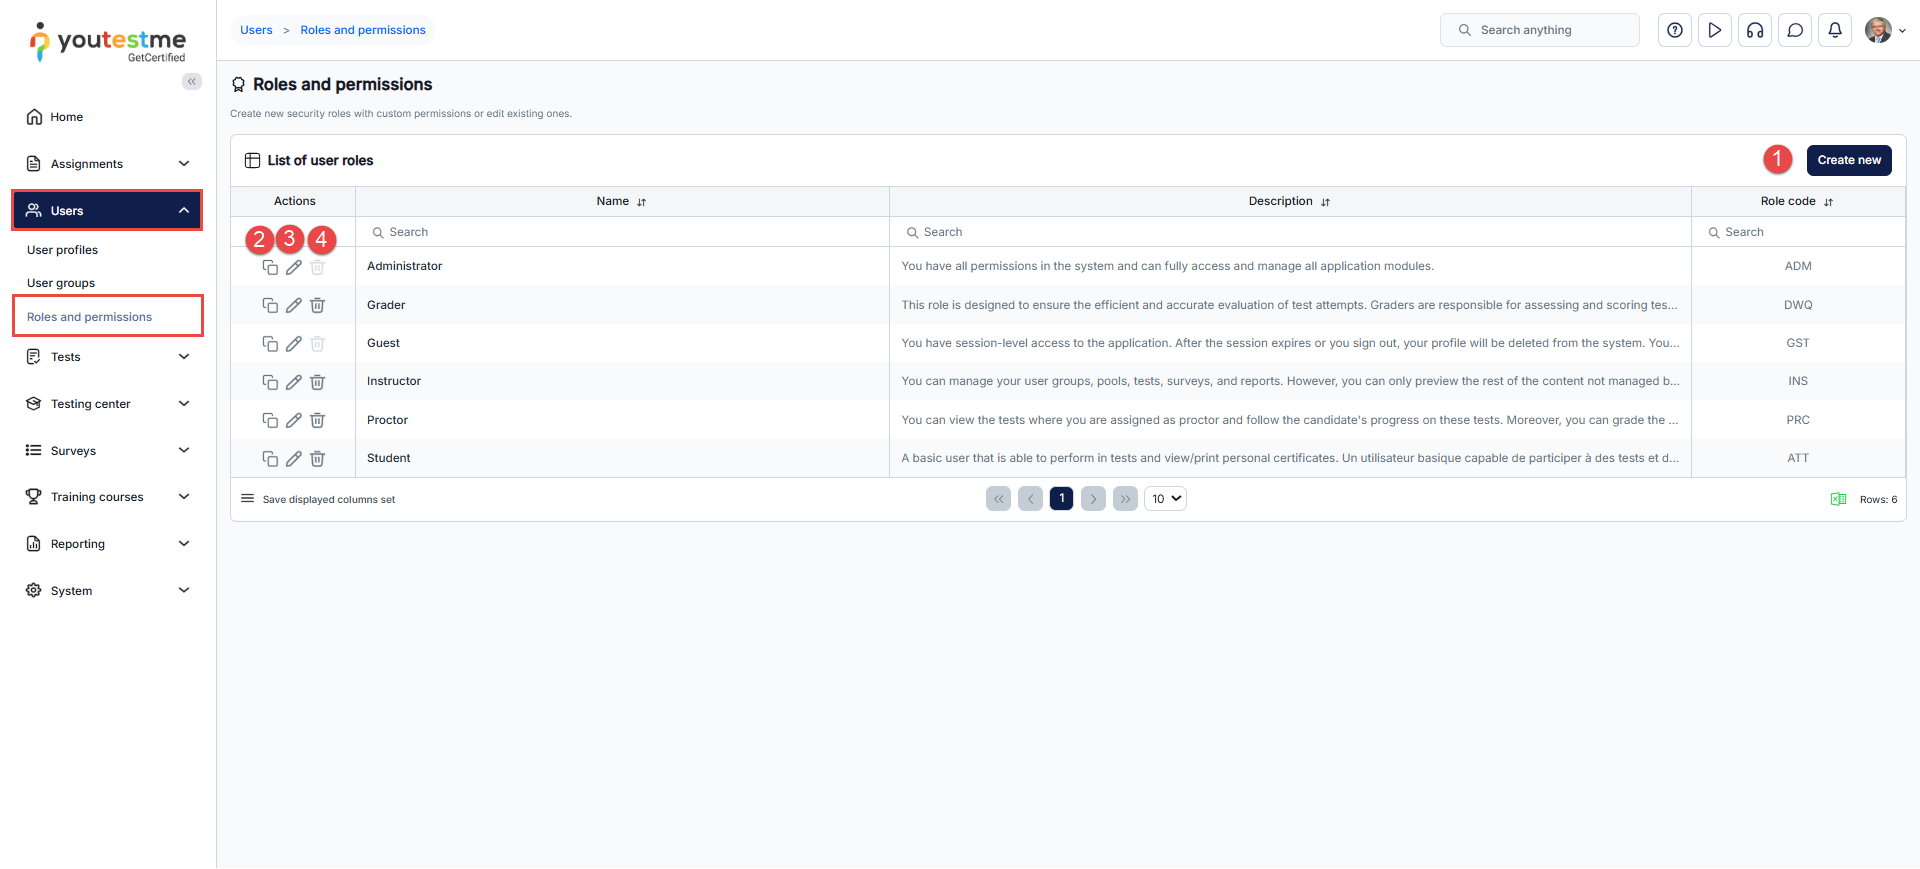
From the Roles and Permissions tab under Users, you can:
- Create a new role
- Copy a role
- Edit a role
- Delete a role
Role Settings
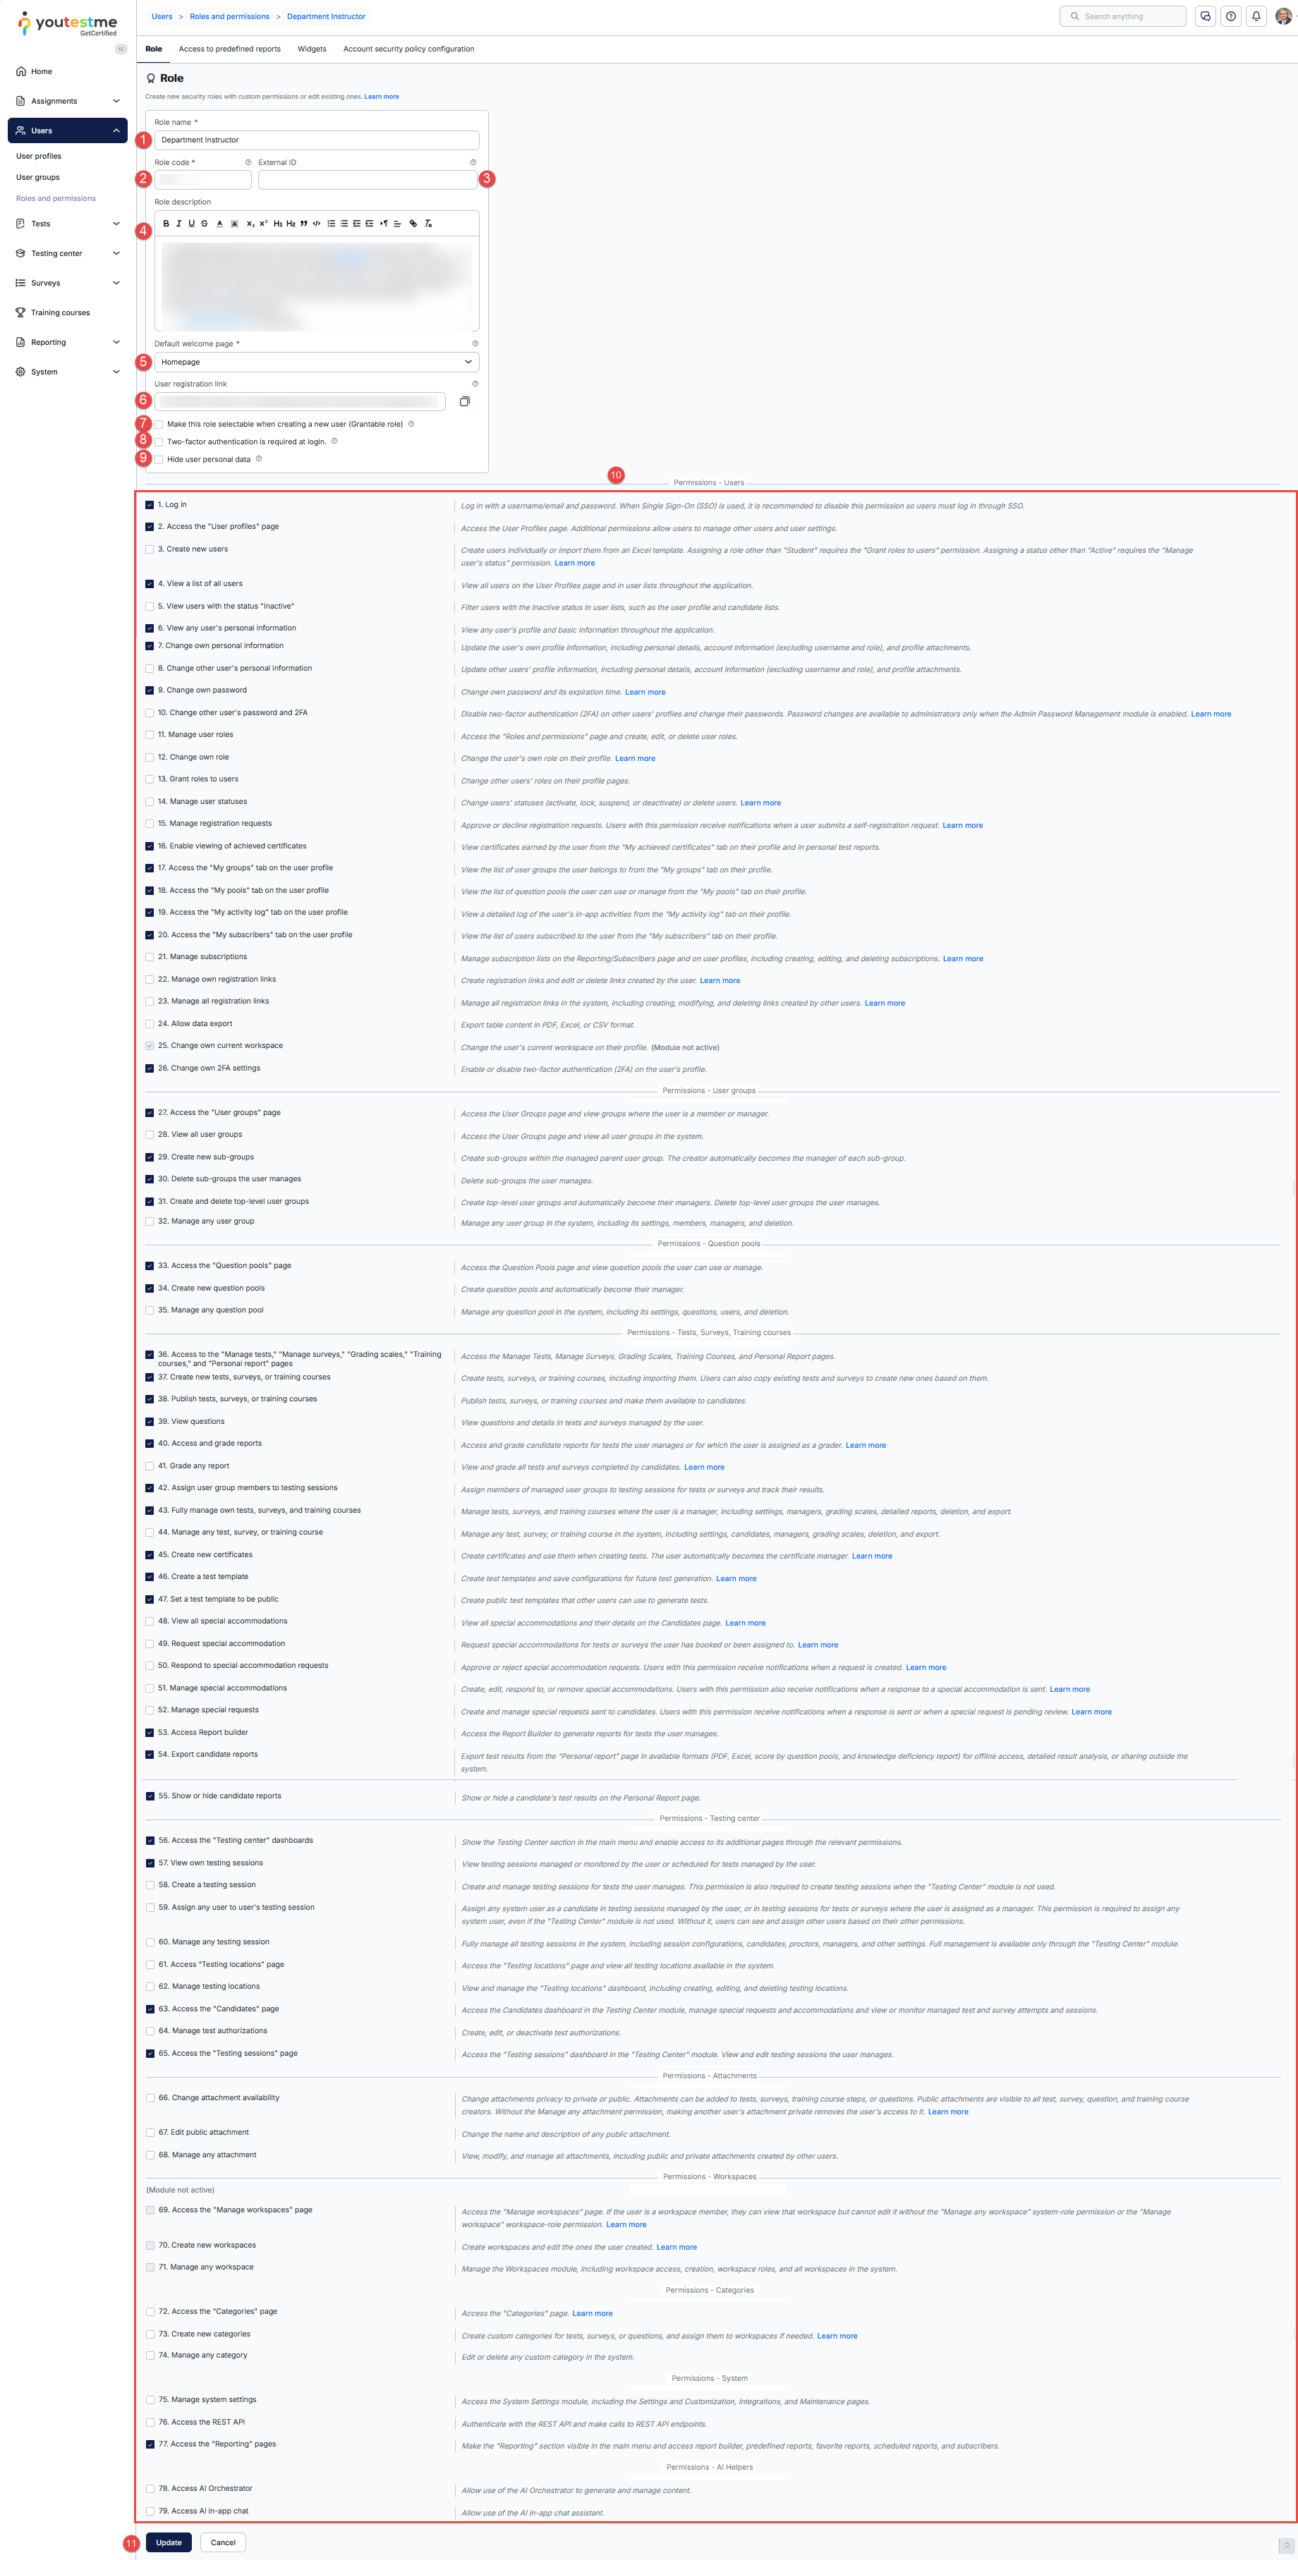
When creating or editing a role, the following settings are available:
- Role Name – The displayed name of the role.
- Role Code – A unique, system-generated code that cannot be edited and is required when importing users via an Excel template.
- External ID – An optional identifier for integrating with external systems.
- Role Description – A short text displayed in the welcome message on the user’s home page.
- Landing Page – Defines the first page a user with this role sees after logging in.
- User Registration Link – Generate and share a link that allows new users to register directly under this role.
- Grantable Role –If a user has permission to create a new user (12. Create new users – enabled) but no permission to assign roles (3. Grant roles to users – disabled), they can select any role labeled as a Grantable role when creating a new user.
- Two-Factor Authentication – Require users assigned to this role to complete two-factor authentication upon login. If two-factor authentication has not been set up, users will be prompted to configure it before proceeding. Please note that this option is applicable only when a standard login with credentials is used. For more information on how to configure two-factor authentication, please refer to this article.
- Hide user personal data – When this option is enabled for a role, users assigned to that role will not be able to view users’ personal data in the application or access it through exports, including information such as username, first name, last name, address, etc.
- Permissions – Select specific actions and data this role can access within the system.
- Click the Create/Update button to create/ update the role.
Note: Each user can have only one role assigned at a time. If a user requires permissions associated with multiple roles, modify the permissions of the assigned role or create a custom role that includes the required permissions.
Note: Editing an existing system role follows the same process as creating a new one.
Accessing predefined reports
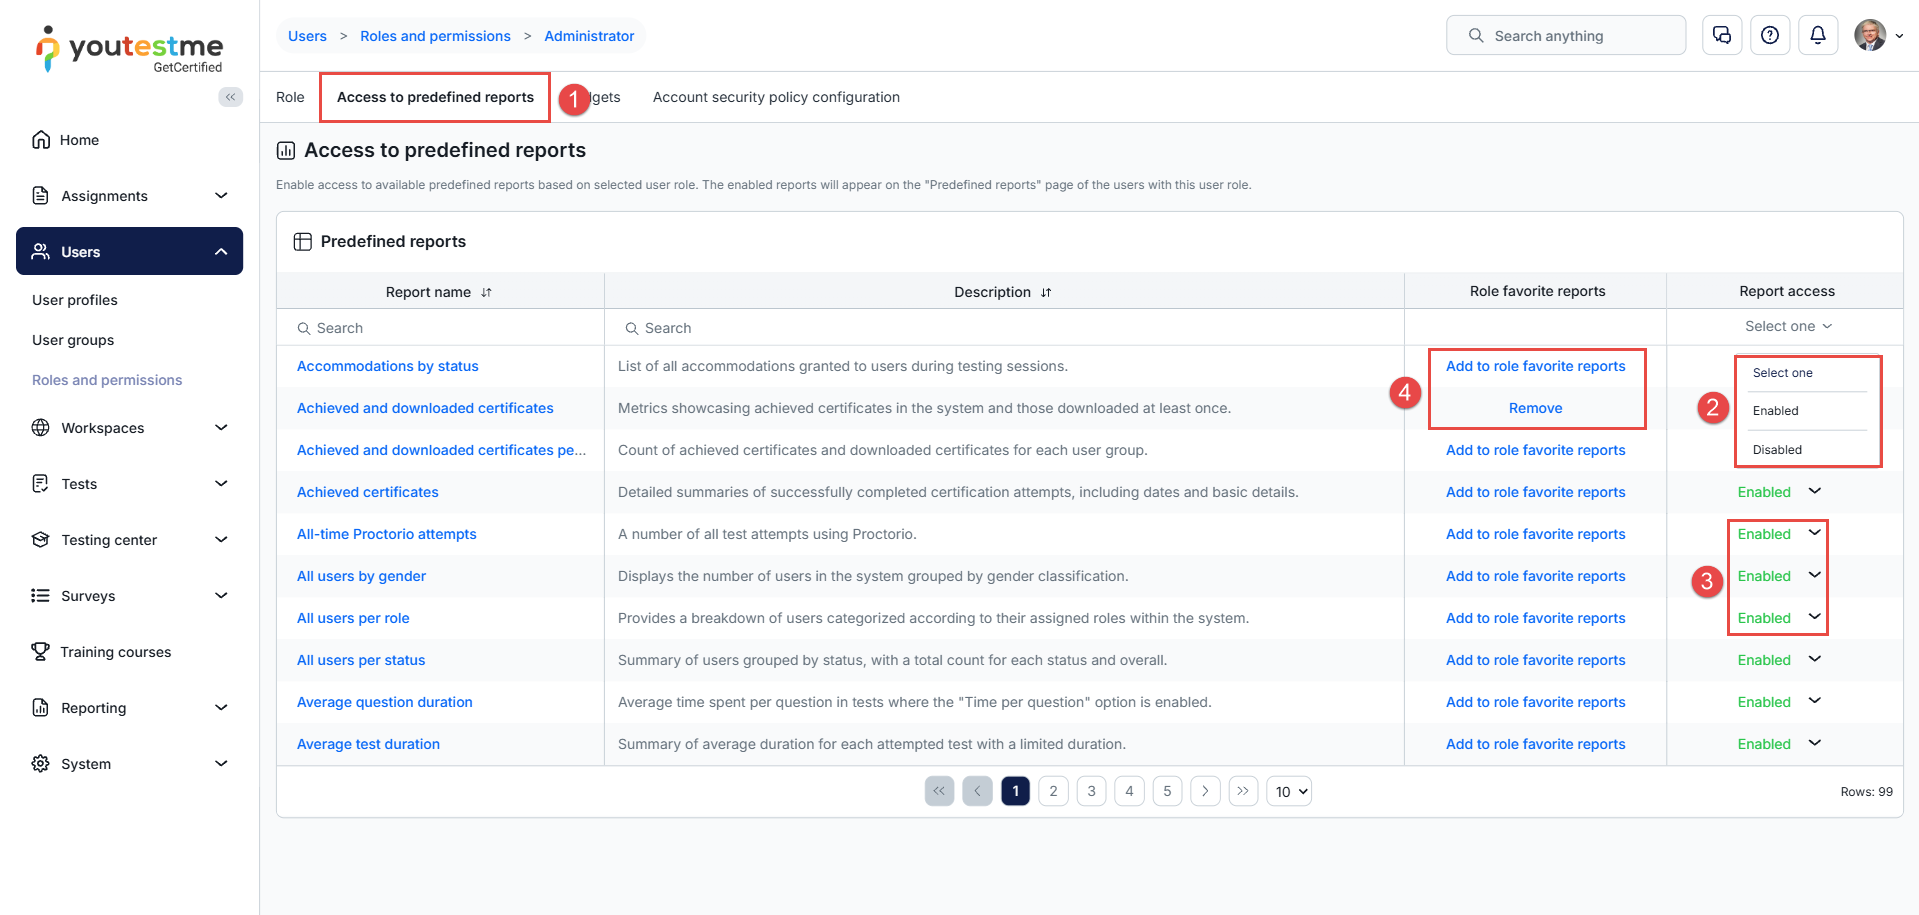
Determine which reports users with this role can access in the Predefined reports section.
To grant access to predefined reports:
- Navigate to the Access to predefined reports tab.
- Filter the table, displaying reports for which the user has either been granted access or not.
- Control access to a specific report by setting it to Enabled or Disabled.
- To mark specific reports as default favorite reports for that role, click the Add to role favorite reports button. Or click the Remove button to delete the report from the favorite report list.
Widgets
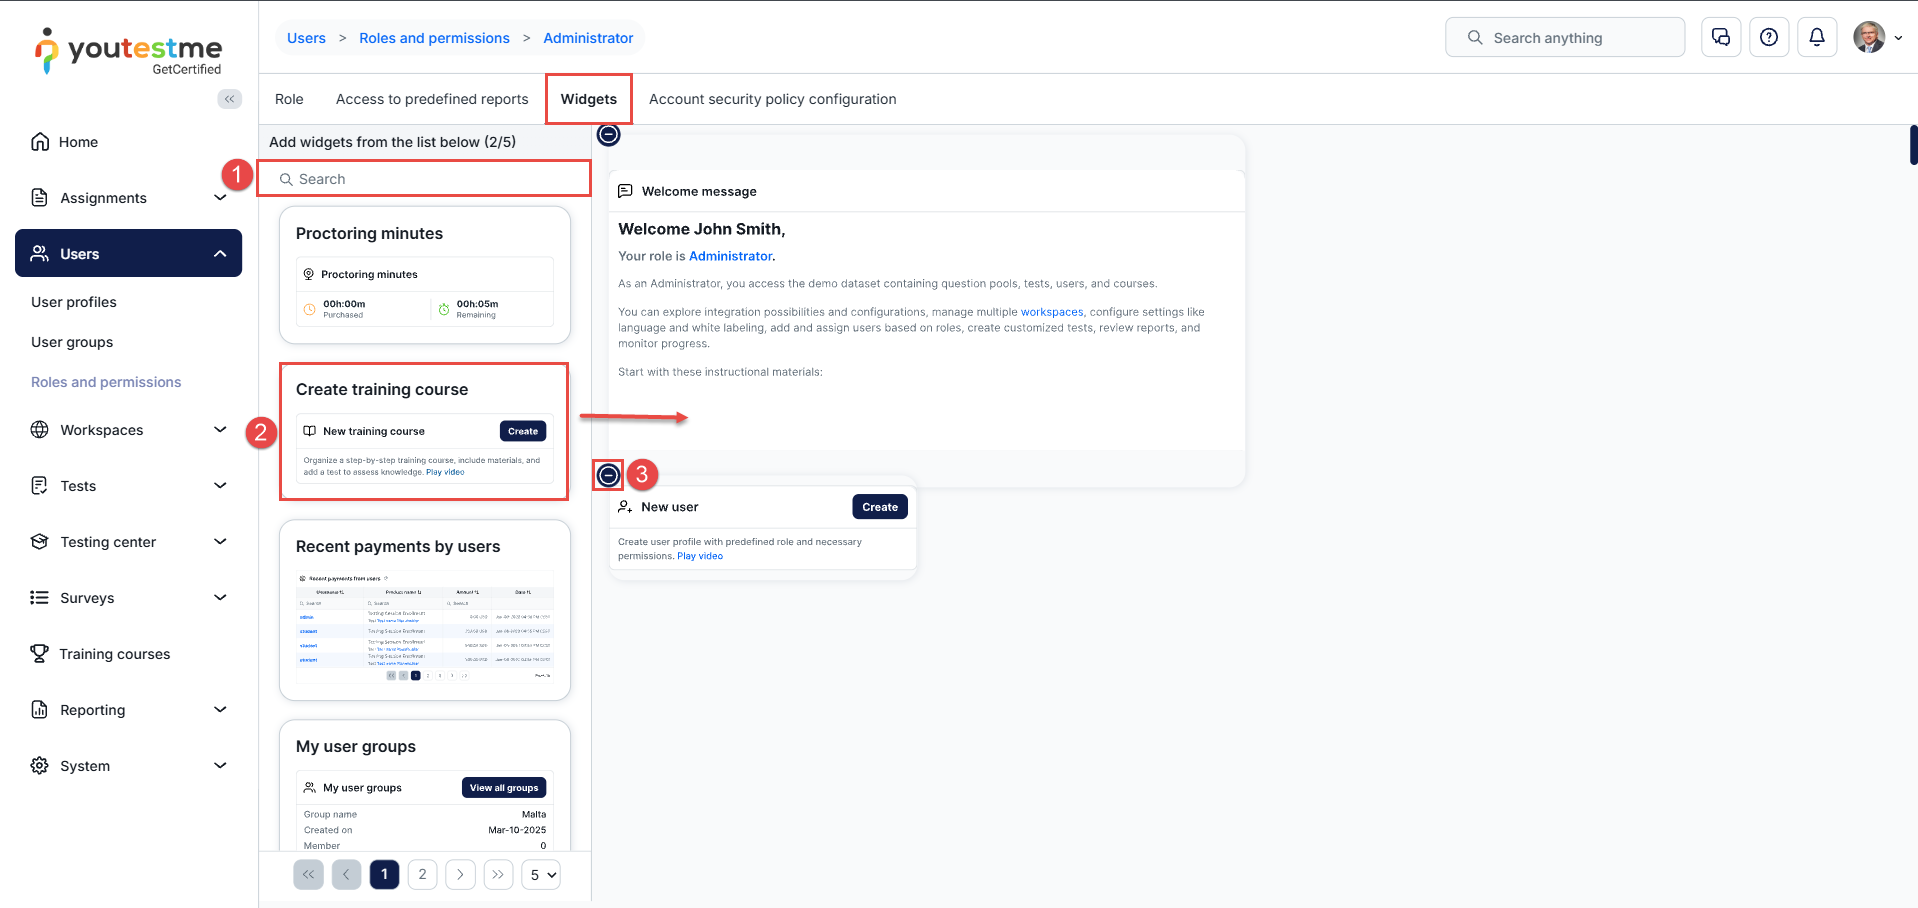
Widgets provide quick access to the frequently used application functions directly from the home page.
The configuration of widgets on the homepage can be tailored to your preferences:
- Use the search bar to find a specific widget from the Available widgets.
- Drag and drop the widget into the blank space on the right side.
- To remove a widget, click on the minus button in the top-left corner of the widget.
For more information on how to use widgets, please check this article.
Account security policy configuration
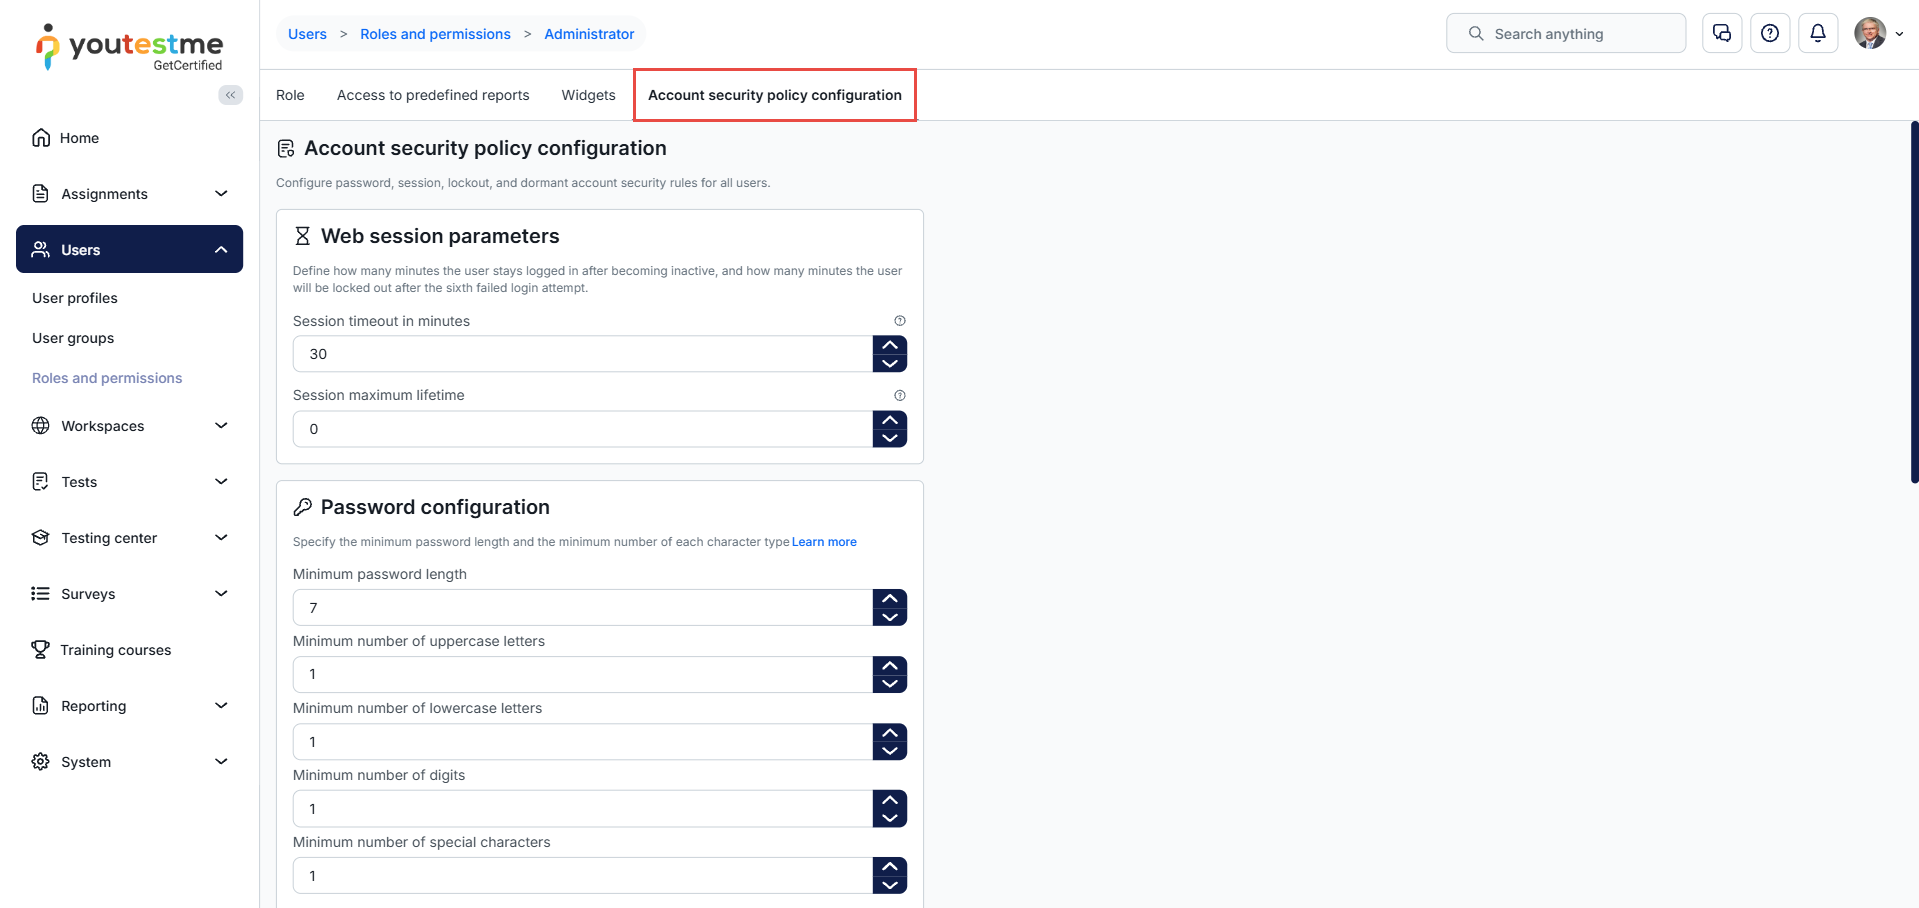
This section allows administrators to configure security policies for a specific role, including session timeouts, password complexity and lifecycle requirements, account lockout rules, and dormant account settings.
Security policies can be customized for each role or inherited from the global system settings using the Use Global Settings option.
Note: The Password reset link duration setting can only be configured at the global level and applies to all users.
For detailed instructions and explanations of each setting, please refer to the Account Security Policy Configuration article.
Conclusion
Roles and permissions allow administrators to manage user access and customize the application experience based on different responsibilities and organizational needs.
By using predefined or custom roles, administrators can control user permissions, configure authentication and account security policies, manage access to reports, and customize landing pages and homepage widgets. These settings help ensure that users have access to the appropriate features and information while maintaining consistent security and access controls across the application.